mimiclem.me
  • Communities
  • Create Post
  • Create Community
  • heart
    Support Lemmy
  • search
    Search
  • Login
  • Sign Up
FenrirIII@lemmy.world to iiiiiiitttttttttttt@programming.dev · 9 days ago

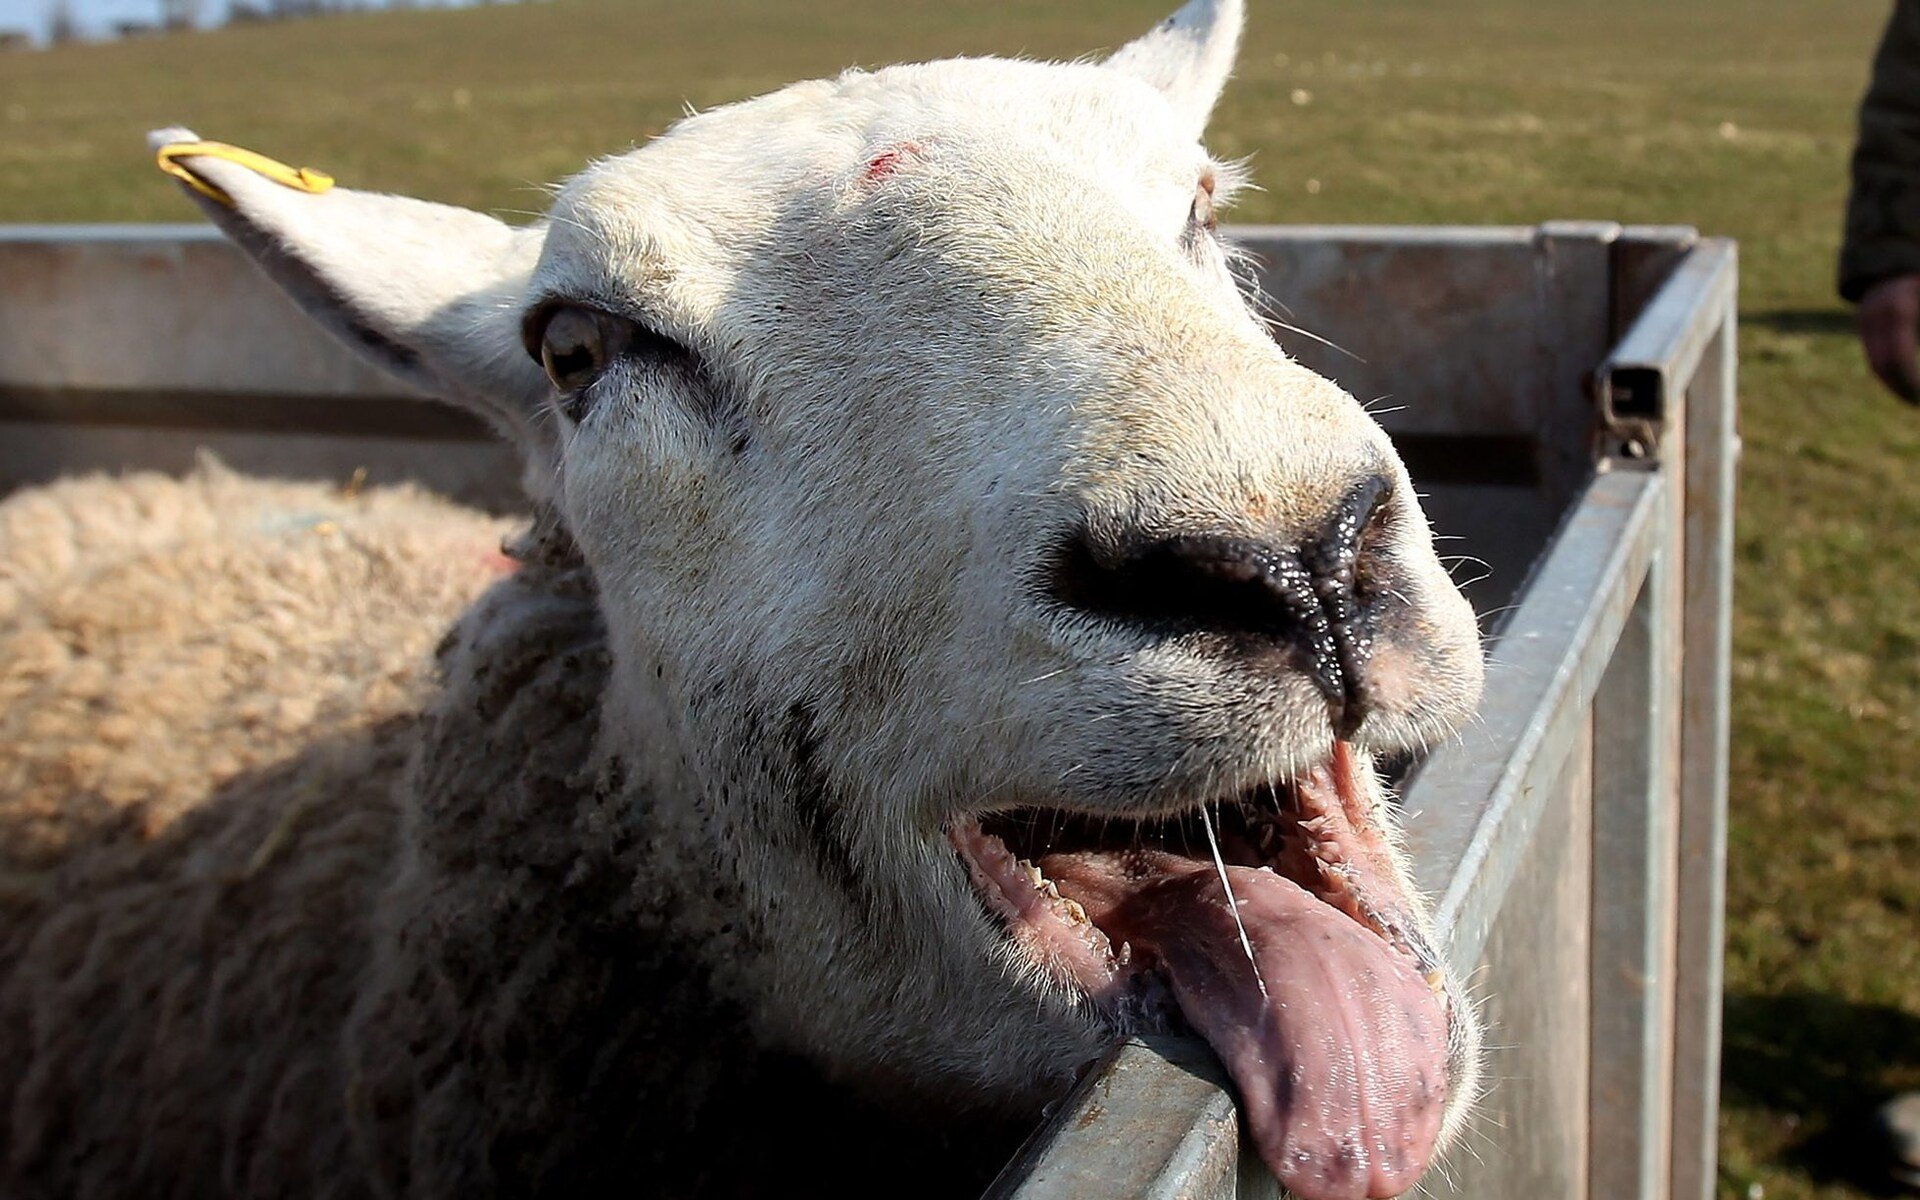
If your computer was alive you would strangle it

lemmy.world

message-square
10
link
fedilink
  • cross-posted to:
  • [email protected]
1

If your computer was alive you would strangle it

lemmy.world

FenrirIII@lemmy.world to iiiiiiitttttttttttt@programming.dev · 9 days ago
message-square
10
link
fedilink
  • cross-posted to:
  • [email protected]

cross-posted from: https://lemmy.world/post/53941877

alert-triangle
You must log in or register to comment.
  • wopalopa@lemmy.world
    link
    fedilink
    arrow-up
    0
    ·
    9 days ago

    “we just had a breach and soft forcing users to change their credentials”

    • T. Hex@lemmy.dbzer0.com
      link
      fedilink
      arrow-up
      0
      ·
      9 days ago

      It legit pisses me off when a site has the gall to claim I forgot my password. My password manager did not forget!!

  • flameleaf@programming.dev
    link
    fedilink
    English
    arrow-up
    0
    ·
    9 days ago

    Don’t tempt me

  • raman_klogius@ani.social
    link
    fedilink
    English
    arrow-up
    0
    ·
    9 days ago

    IT devs who wrote oldpassword===newpassword checks should be tarred feathered hung drawn and quartered, in that order.

    • purplemonkeymad@programming.dev
      link
      fedilink
      arrow-up
      0
      ·
      9 days ago

      Yeah! They should be checking a list of old hashes, so that none of the previous passwords can be used!

    • dou9m@lemmy.ca
      link
      fedilink
      arrow-up
      0
      ·
      9 days ago

      Nah, use a password manager and stop using that garbage collection of characters you’ve used for over a decade.

      • raman_klogius@ani.social
        link
        fedilink
        English
        arrow-up
        0
        ·
        9 days ago

        Password managers don’t protect against passwords being stored in plaintext on the server side… Which my main comment implies.

        • ExtraMedicated@lemmy.world
          link
          fedilink
          English
          arrow-up
          0
          ·
          9 days ago

          If I had to implement a same password check, I would simply check if the new password works to authenticate the user. If it doesn’t, then it’s different. There’s no reason or excuse to ever store plaintext passwords.

    • sem@lemmy.blahaj.zone
      link
      fedilink
      arrow-up
      0
      ·
      9 days ago

      They should also fire the ones who make it so the correct password fails when you enter it.

  • X@piefed.world
    link
    fedilink
    English
    arrow-up
    0
    ·
    9 days ago

    (enters “4”)
    Notification: Your password has changed

iiiiiiitttttttttttt@programming.dev

iiiiiiitttttttttttt@programming.dev

Subscribe from Remote Instance

Create a post
You are not logged in. However you can subscribe from another Fediverse account, for example Lemmy or Mastodon. To do this, paste the following into the search field of your instance: [email protected]

you know the computer thing is it plugged in?

A community for memes and posts about tech and IT related rage.

Visibility: Public
globe

This community can be federated to other instances and be posted/commented in by their users.

  • 1 user / day
  • 14 users / week
  • 14 users / month
  • 55 users / 6 months
  • 0 local subscribers
  • 1.81K subscribers
  • 88 Posts
  • 230 Comments
  • Modlog
  • mods:
  • irelephant [he/him]@programming.dev
  • Shivering@programming.dev
  • neidu3@sh.itjust.works
  • King Tootsie@programming.dev
  • AnarchistArtificer@slrpnk.net
  • BE: 0.19.20
  • Modlog
  • Instances
  • Docs
  • Code
  • join-lemmy.org